Key takeaways
- Server-side tracking changes how events are collected and routed; it does not eliminate privacy restrictions.
- Shopify purchase accuracy depends on event origins, checkout constraints, consent and event identity.
- Meta browser/server deduplication requires consistent event names and event IDs.
- A successful implementation is verified across Shopify, GA4 and destination diagnostics, not judged by a promised uplift percentage.
What server-side tracking actually changes
Traditional browser tags send requests directly from the browser to multiple vendors. In a server-side setup, a collection endpoint receives events and a server container transforms and routes permitted data to destinations.
This can improve control over payloads, reduce some browser-to-vendor requests and support first-party collection strategies. It cannot reliably restore events blocked before collection, and results depend on the browser, implementation and consent choices.
Shopify architecture and event sources
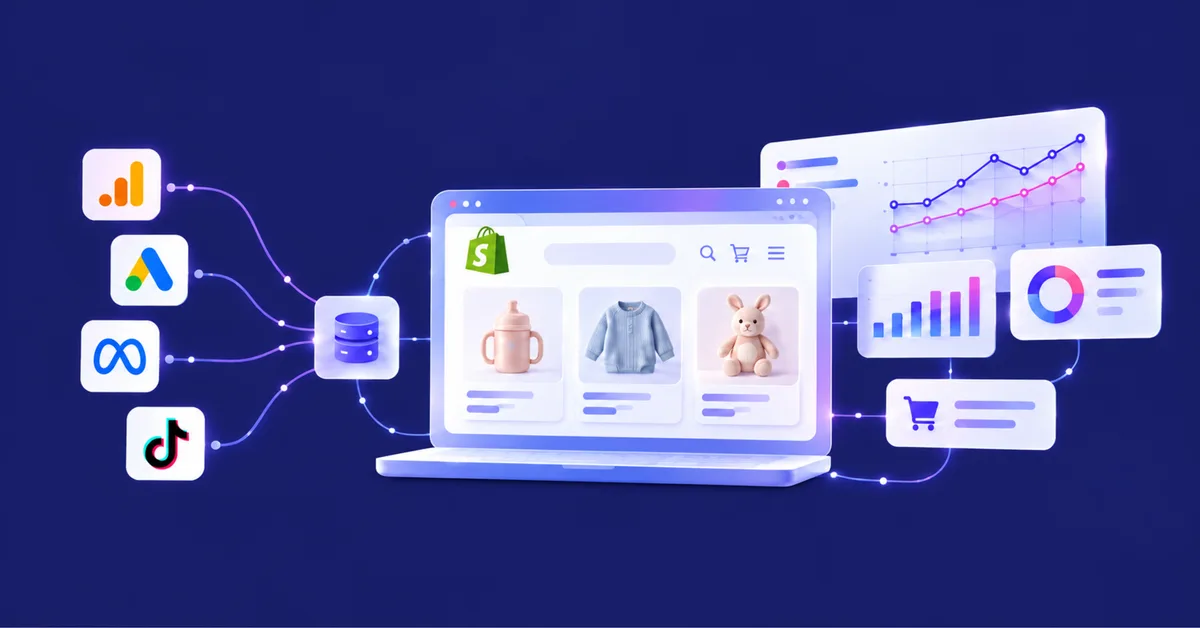
Shopify Customer Events and web pixels provide a supported event framework, including checkout events subject to the shop’s configuration and Shopify platform constraints. A storefront dataLayer alone may not capture every checkout step.
A practical architecture may involve a Shopify-compatible collection mechanism, GA4 or another event transport, a server-side Google Tag Manager container hosted by Stape, and destination tags or API clients. The exact wiring must be verified for the Shopify plan, checkout setup and chosen integrations.
Event specification before implementation
Define an event contract: event_name, event_id, timestamp, order_id, currency, value, item identifiers, consent state and permissible user identifiers. Document the source of truth for each field.
For purchase, ensure order_id is stable and distinct from event_id. Repeated page views or retries must not create new unique purchases in downstream systems. Avoid sending raw personal data to analytics endpoints not designed to receive it.


Meta CAPI and deduplication
For browser Pixel and Conversions API events representing the same action, align the event name and event_id according to Meta’s deduplication requirements. Generate the identifier once and propagate it across paths.
Event Match Quality describes matching signals and is not the same as deduplication health or incrementality. Hash eligible user data only where appropriate, and do not confuse hashing with a legal basis for processing.
Consent, privacy and governance
Consent Mode v2 includes consent signals such as ad_storage, analytics_storage, ad_user_data and ad_personalization. Map these signals to your CMP and destination behavior; implementation requirements vary by region and vendor.
Quebec Law 25 and GDPR compliance cannot be inferred from the mere use of a server endpoint. Document collection purposes, vendor sharing, retention, access controls and consent behavior with legal counsel where appropriate.
Implementation and QA checklist
- Inventory all existing pixels, apps, web pixels and purchase events.
- Define event ownership and IDs.
- Configure the server endpoint and custom domain.
- Implement consent propagation.
- Map destination tags and deduplication.
- Test checkout paths, declined payments, refunds and repeat purchases.
- Monitor production diagnostics after release.
In GTM Preview and server Preview, confirm incoming requests, transformed parameters and outgoing requests. In Meta Events Manager, inspect test events and deduplication warnings; in GA4 DebugView, inspect event names and parameters. Reconcile orders over a consistent time window.
Measurement and troubleshooting
A discrepancy between Shopify orders and Meta-attributed purchases is not automatically a tracking bug: attribution windows, modeled conversions, reporting time zones and refunds differ. Use event-level testing and order IDs to diagnose instrumentation.
Track event coverage, missing purchase values, duplicate rate, consent rejection behavior, destination errors and page performance. Establish a baseline before claiming improvement.
| QA check | Expected behavior | Where to inspect |
|---|---|---|
| Purchase event ID | Shared between browser and server copies | Pixel/CAPI payloads |
| Order ID | Stable for one order | Shopify + event logs |
| Consent denied | Only permitted processing occurs | CMP + network + server |
| Currency and value | Match transaction definition | Shopify + GA4 |
| Retries | Do not inflate conversions | Server logs + destination |
Common mistakes and limitations
- Duplicate Shopify apps firing the same event.
- Generating new event IDs on server retries.
- Missing consent states.
- Sending purchase values in mixed currencies.
- Assuming every checkout event is accessible through storefront GTM.
- Enabling user-data forwarding without a lawful basis.
Frequently asked questions
Does server-side tracking bypass consent?
No. Applicable consent requirements remain in force regardless of the transport path.
Will Meta and Shopify purchase counts match?
Not necessarily. Attribution windows, modeled conversions, refunds and time zones differ.
Is a custom subdomain enough?
No. Event design, consent propagation, deduplication and destination configuration are essential.